Home / Guides / NIST 800-171 and CMMC
GuideCyber requirements,
and what purchasing owns
Most of this sits with IT. The parts that sit with purchasing are identifying which subcontractors handle protected information, flowing the obligations down, and being able to show you did.
NIST SP 800-171 sets out security requirements for protecting controlled unclassified information in non federal systems, and CMMC is the Department's programme for verifying that contractors meet them. On 13 July 2026 the Department of War suspended CMMC Phase II and later milestones pending review. Phase I self-assessment requirements and the underlying safeguarding obligations remain in force.
As at August 2026
This area has moved repeatedly and is under active review, so treat any position as current only at the date shown and verify before acting on it.
As at August 2026
This area has moved repeatedly and is under active review, so treat any position as current only at the date shown and verify before acting on it.
- NIST SP 800-171 requirements still apply
- CMMC Phase I in force; Phase II suspended
- Existing contract terms are unchanged
| Element | Status |
|---|---|
| NIST SP 800-171 | The underlying security requirements for protecting controlled unclassified information in non federal systems. Unaffected by the CMMC programme changes |
| CMMC Phase I | In force. Level 1 and Level 2 self-assessment requirements, safeguarding obligations and annual affirmations continue |
| CMMC Phase II | Suspended with immediate effect on 13 July 2026. This would have required third party assessment as a condition of award from 10 November 2026 |
| Phases III and IV | Pending and future implementation milestones held pending the outcome of a review of the programme |
| Contractual obligations | Unchanged. Terms already in your contracts continue to bind you regardless of the Department's implementation timing |
Four responsibilities that are not IT's
The controls are somebody else's job. The supply chain is yours, and that is the part reviewers ask purchasing about.
Four responsibilities that are not IT's
The controls are somebody else's job. The supply chain is yours, and that is the part reviewers ask purchasing about.
- Identify scope at award
- Evidence the flow-down on the award
- Track status over the life of the award
Assumed to be an IT question
Nobody in purchasing knows which subcontractors will handle protected information, because the question was treated as technical rather than contractual.
Determined at award
Whether a subcontractor will handle protected information is established when the award is placed, and recorded on the purchase record.
Assumed to happen
The required terms are believed to be in the standard clause set without anybody confirming they applied to this particular subcontract.
Confirmed per subcontract
The applicable terms are determined for the award and evidenced on it, in the same way as any other flow-down.
Collected once
A subcontractor's position is established at onboarding and never revisited, so changes over a multi year award go unnoticed.
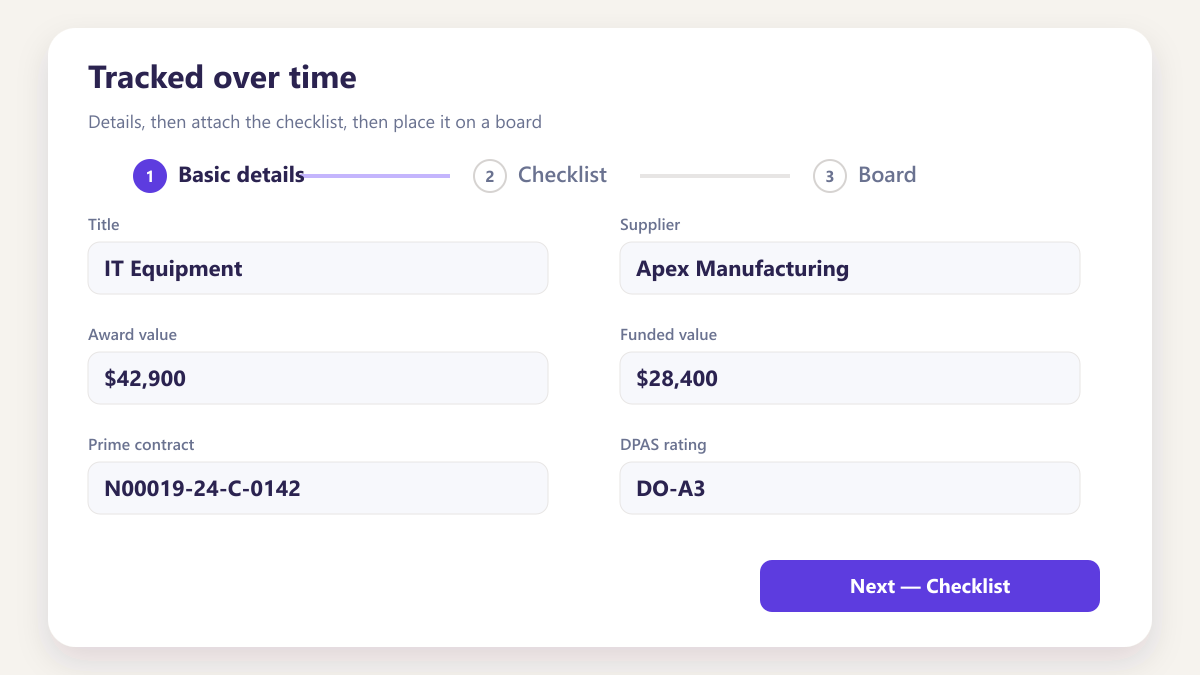
Tracked over time
Status is held against the supplier record with dates, so it is current for as long as the relationship runs rather than accurate on one day.
Waiting for certainty
Because the programme timetable has moved, preparation is paused until the position settles, which leaves contractual obligations unaddressed in the meantime.
Holding the line
Safeguarding and self-assessment duties are maintained regardless of implementation timing, because contract terms are not suspended by a programme review.
Four items on a subcontract touching protected information
| Item | Why |
|---|---|
| Whether the subcontractor will handle protected information | Determined at award rather than discovered later, because it drives everything else |
| Which terms were flowed down | Evidenced on the award in the same way as any other flow-down clause |
| What the subcontractor asserted | Their stated position, held with a date, rather than an assumption carried forward indefinitely |
| How status is monitored | Whether and how the position is revisited over the life of the award |
This programme has changed direction more than once and is under active review. Confirm the current position from official sources before relying on any timetable.
Four things that hold whatever the timetable does
Identify scope at award
Which subcontractors handle protected information is a contractual question, and answering it at award is far easier than reconstructing it.
Learn moreEvidence the flow-down
Required terms passed to a subcontractor should be evidenced on the award like any other clause, not assumed from a standard set.
Learn moreTrack status over time
A position established at onboarding and never revisited is accurate on one day and unknown thereafter.
Learn moreKeep going through the review
Contract terms already agreed continue to bind you regardless of what the implementation timetable does.
Learn moreCommon questions about cyber requirements in purchasing
What is NIST SP 800-171?
What happened to CMMC in 2026?
Does the suspension remove our obligations?
What was Phase II going to require?
What does purchasing own in all this?
Should we pause our preparation?
How current is this page?
Other explainers and the pages they connect to
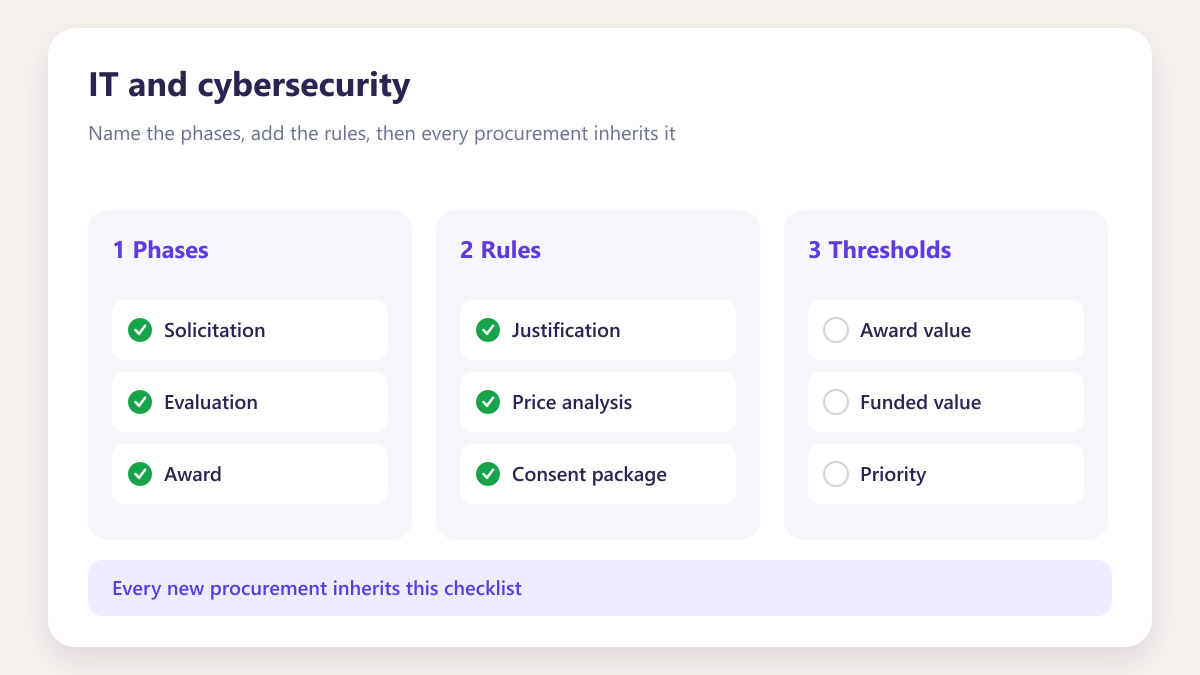
IT and cybersecurity
Purchasing where the supply chain behind an award is examined too.
Learn more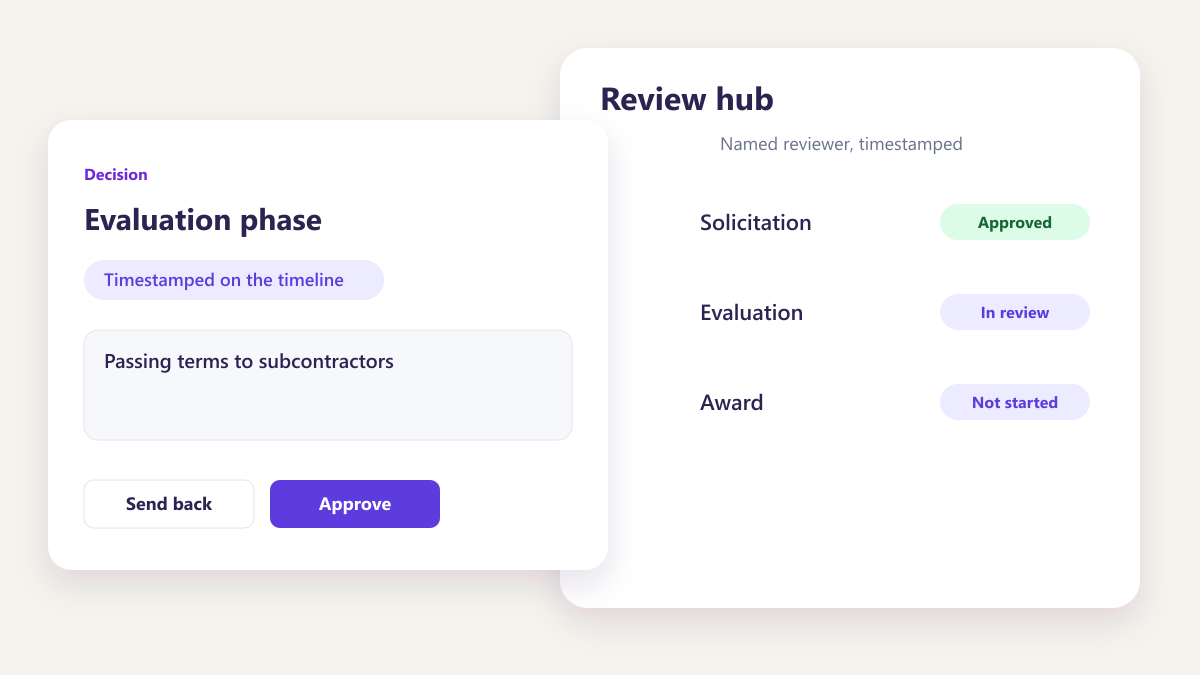
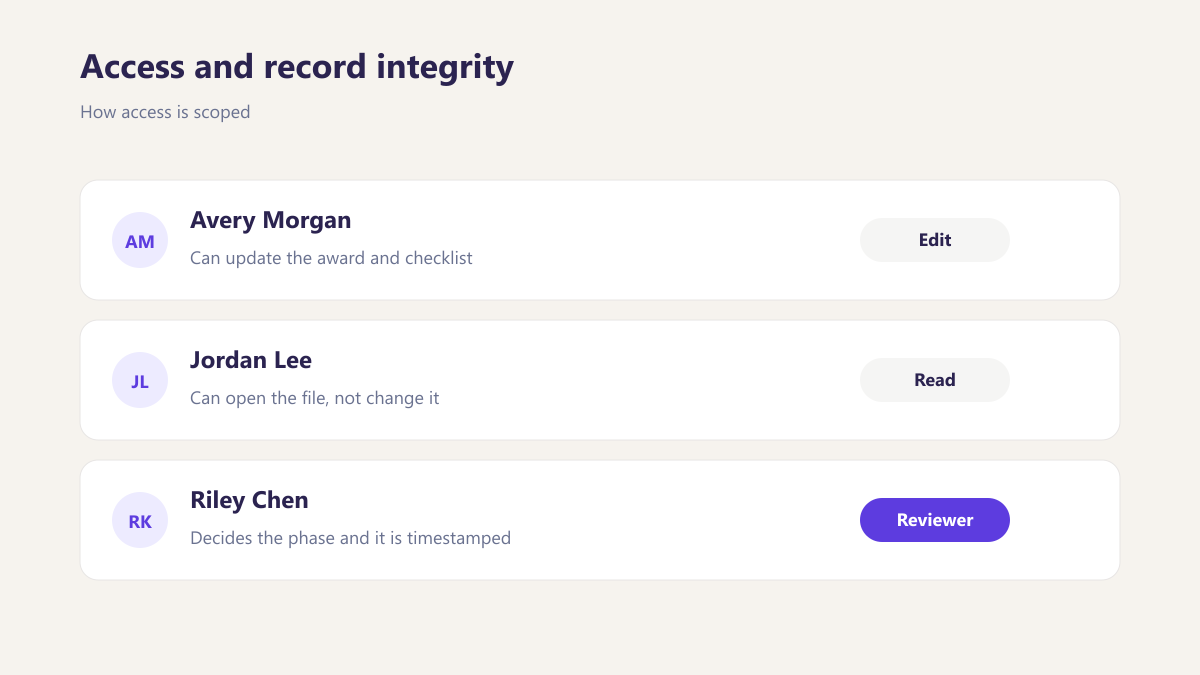
Access and record integrity
How access is scoped and why entries cannot be revised afterwards.
Learn moreWork out what purchasing owns
Bring a subcontract where the position is unclear. We will separate what is an IT question from what belongs in your purchase file.
Book a demo